Ping Identity
This guide connects a PingOne OIDC web application with the generic driver.
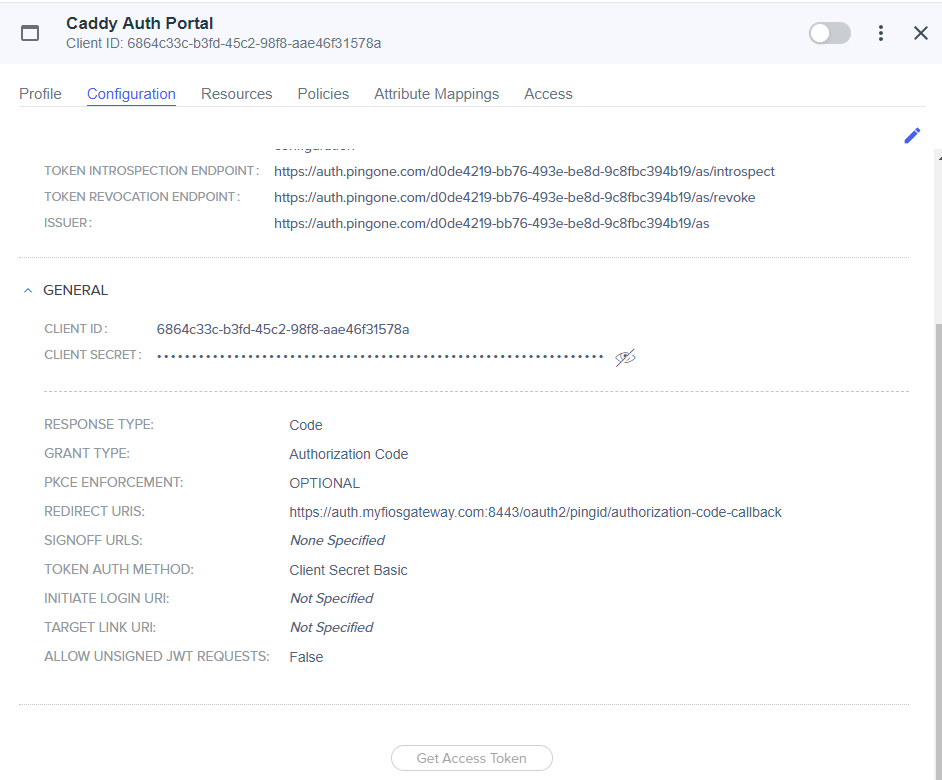
The historical realm name pingid remains in the callback for compatibility;
it does not implement the separate PingID mobile authentication API. PingOne
can enforce its own sign-on/MFA policy before returning an OIDC identity.
Register a confidential web application
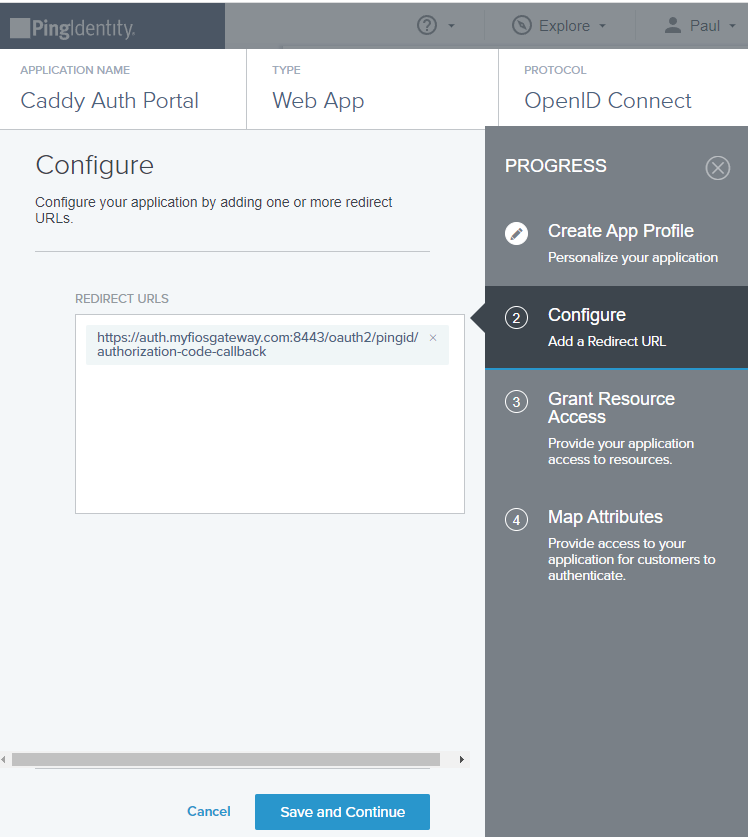
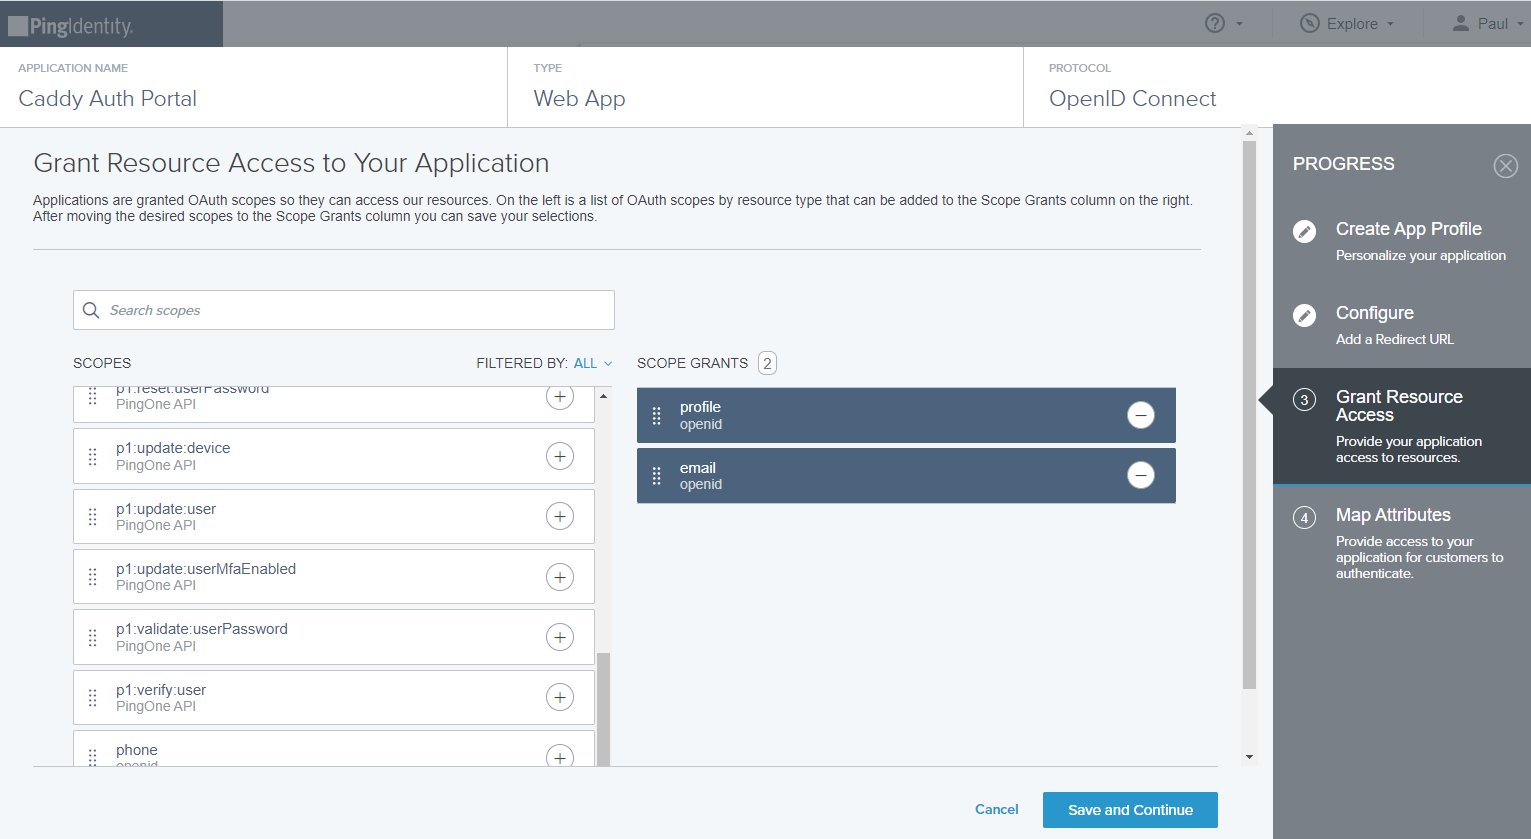
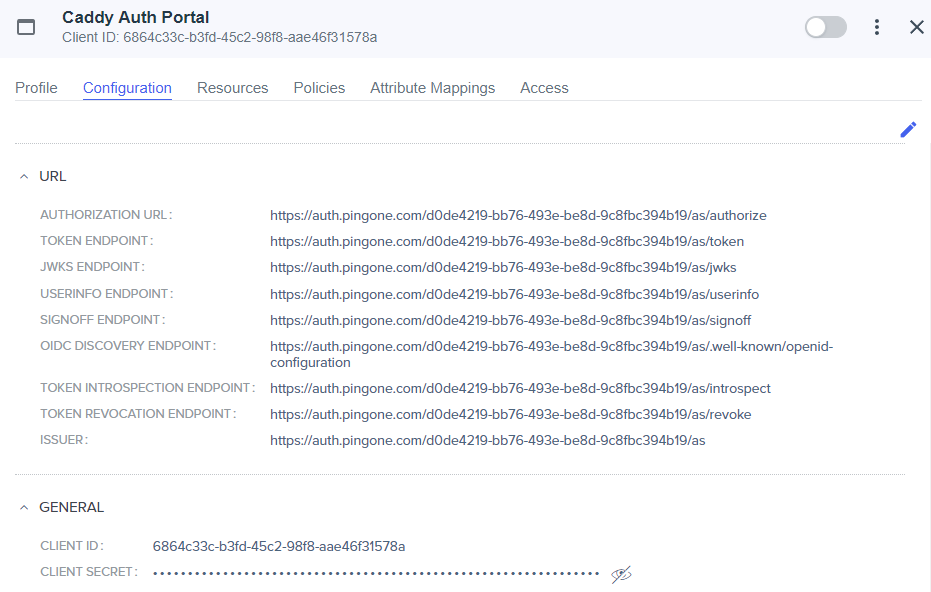
Create an OIDC web application in the intended PingOne environment, enable authorization code, register the callback below, and configure token endpoint authentication as Client Secret Post. PingOne web applications can default to Client Secret Basic; the bundled generic exchange sends the secret in the form body. See PingOne application settings.
https://auth.example.com/auth/oauth2/pingid/authorization-code-callback
Copy the actual issuer and OIDC discovery URL from your environment/application.
Use the region or custom domain PingOne provides. The environment ID and OAuth
client ID are different values; do not construct the issuer from an application
ID. Supply PINGONE_ISSUER, PINGONE_DISCOVERY_URL, PINGONE_CLIENT_ID,
PINGONE_CLIENT_SECRET, and the private AUTHCRUNCH_SIGNING_KEY.
The issuer/discovery values expand before Caddyfile parsing.
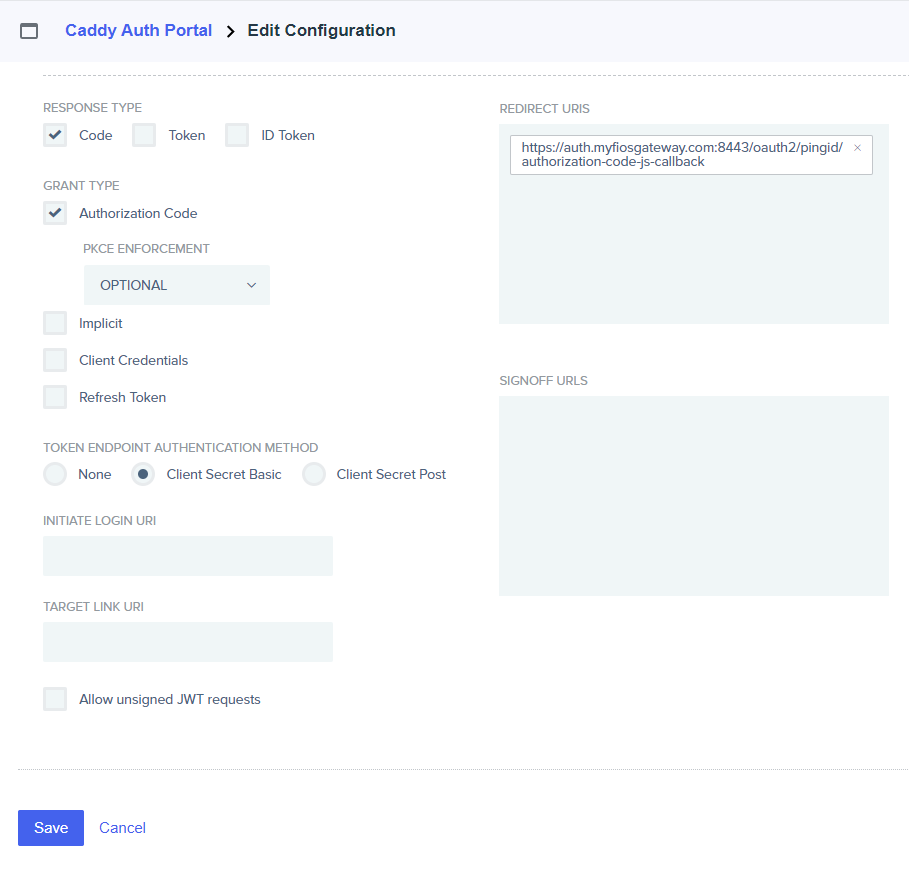
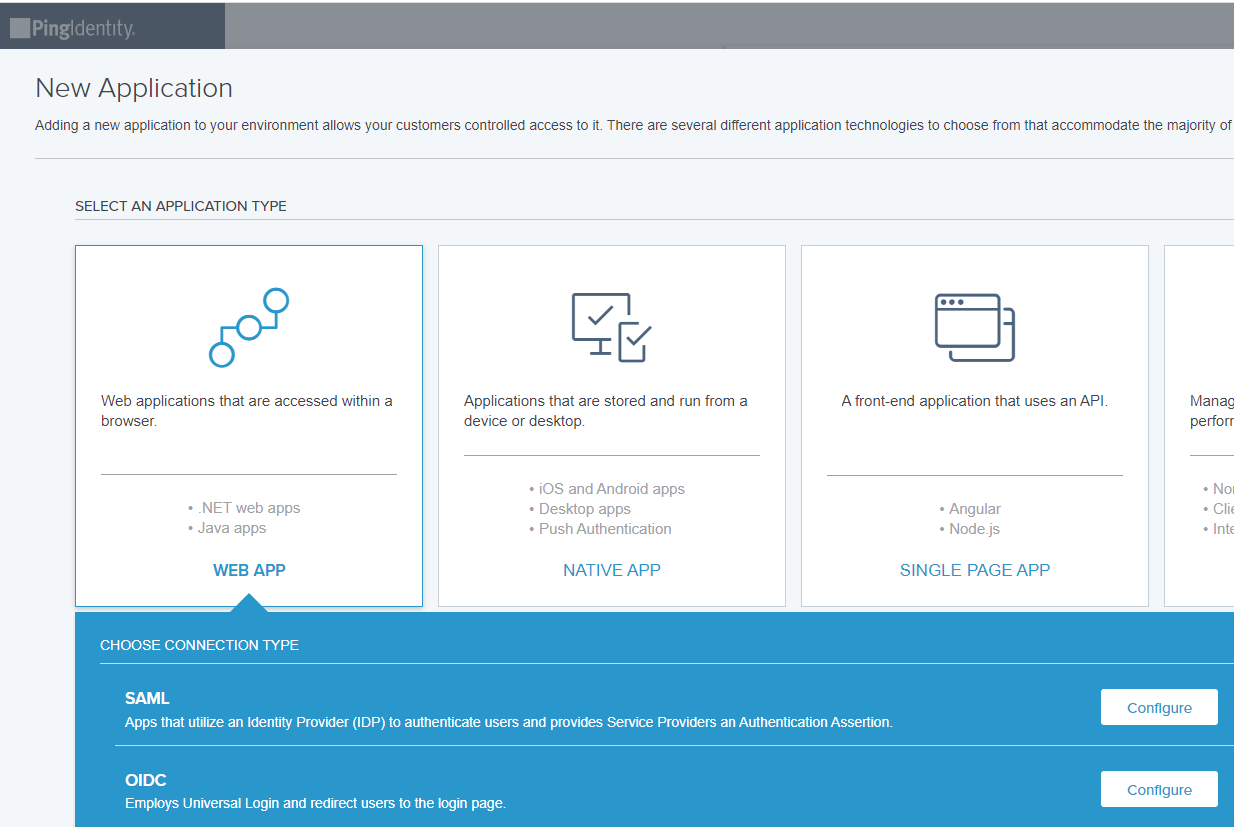
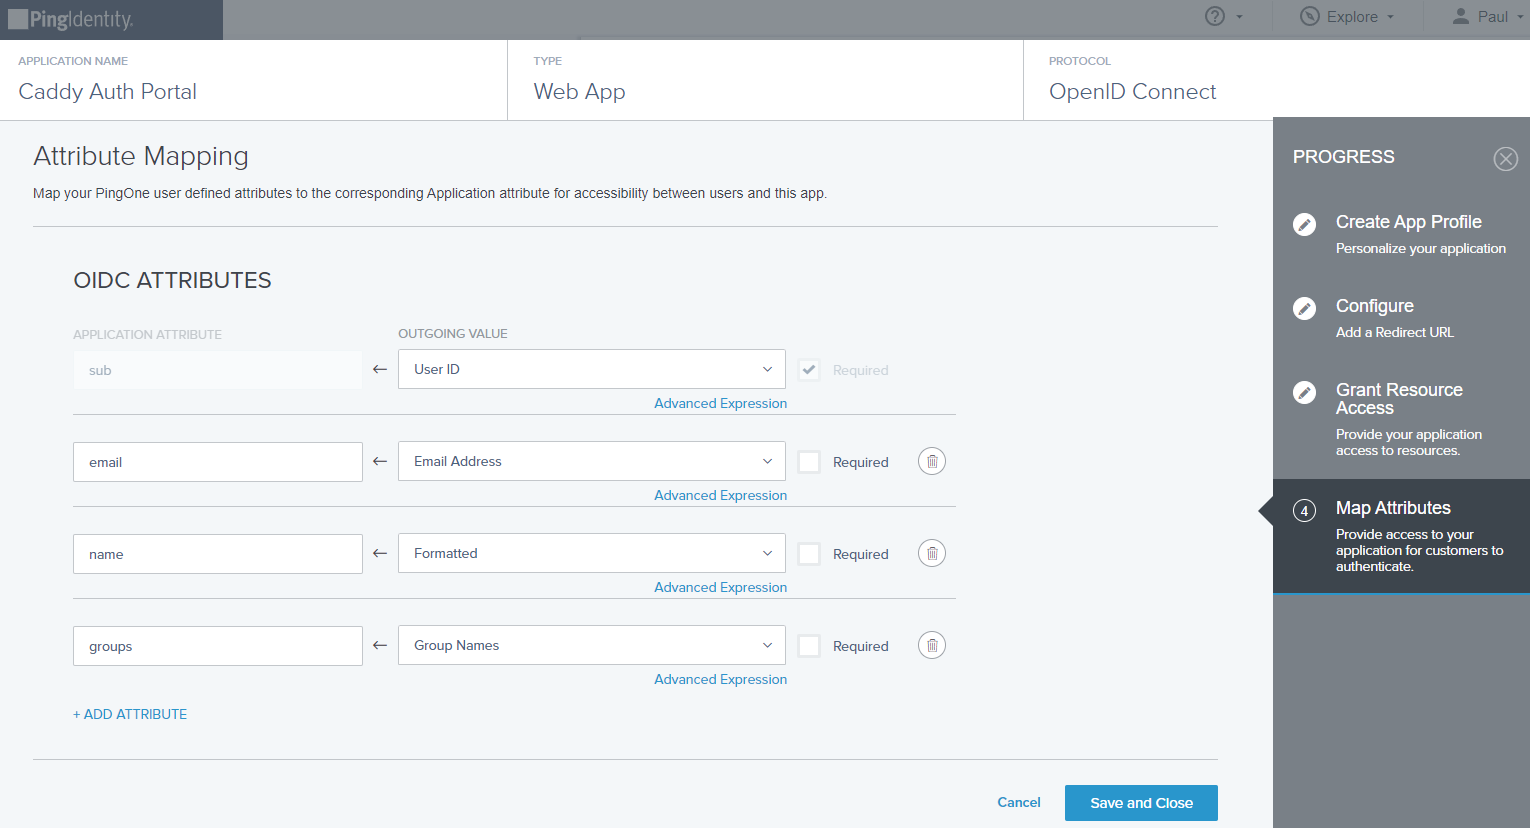
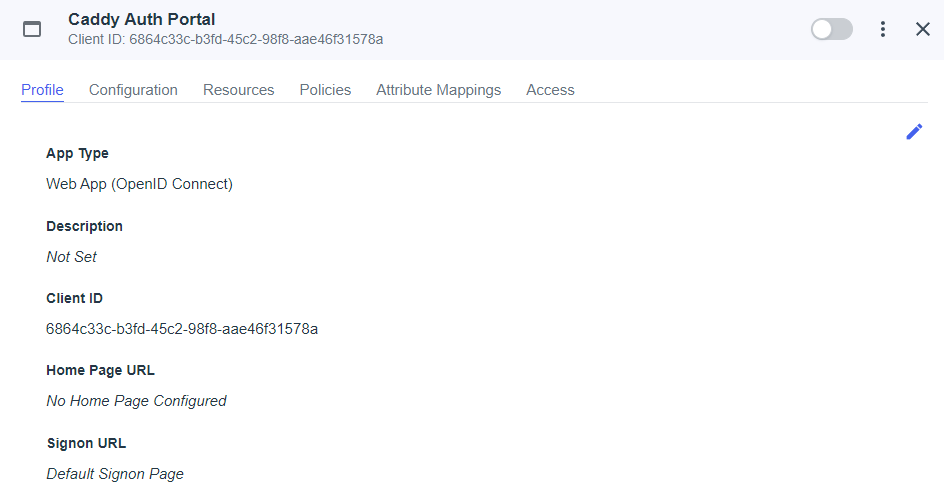
Preserved PingOne setup sequence
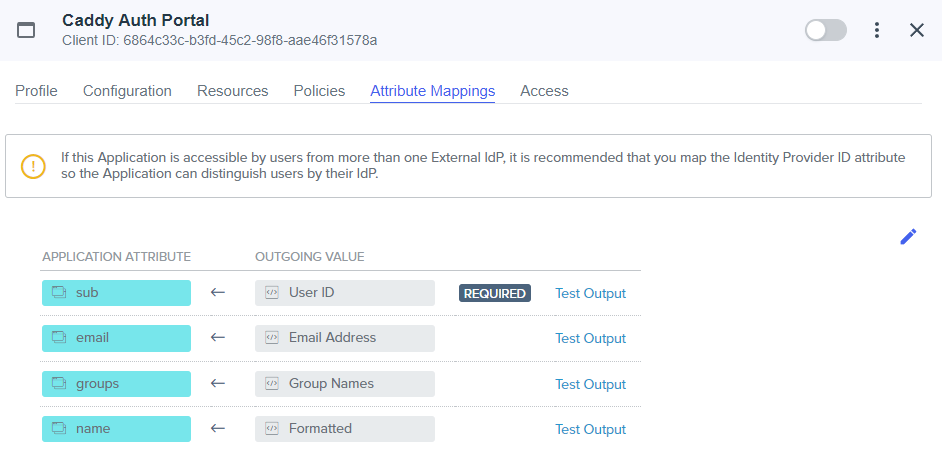
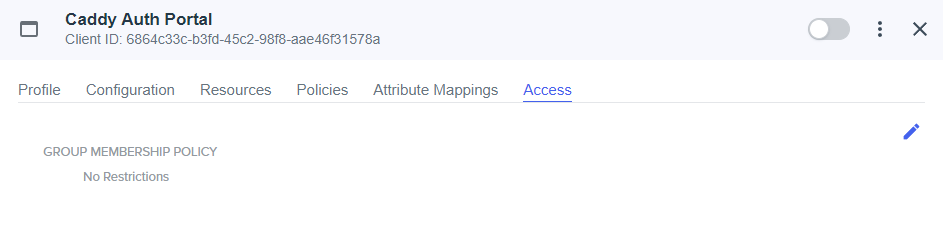
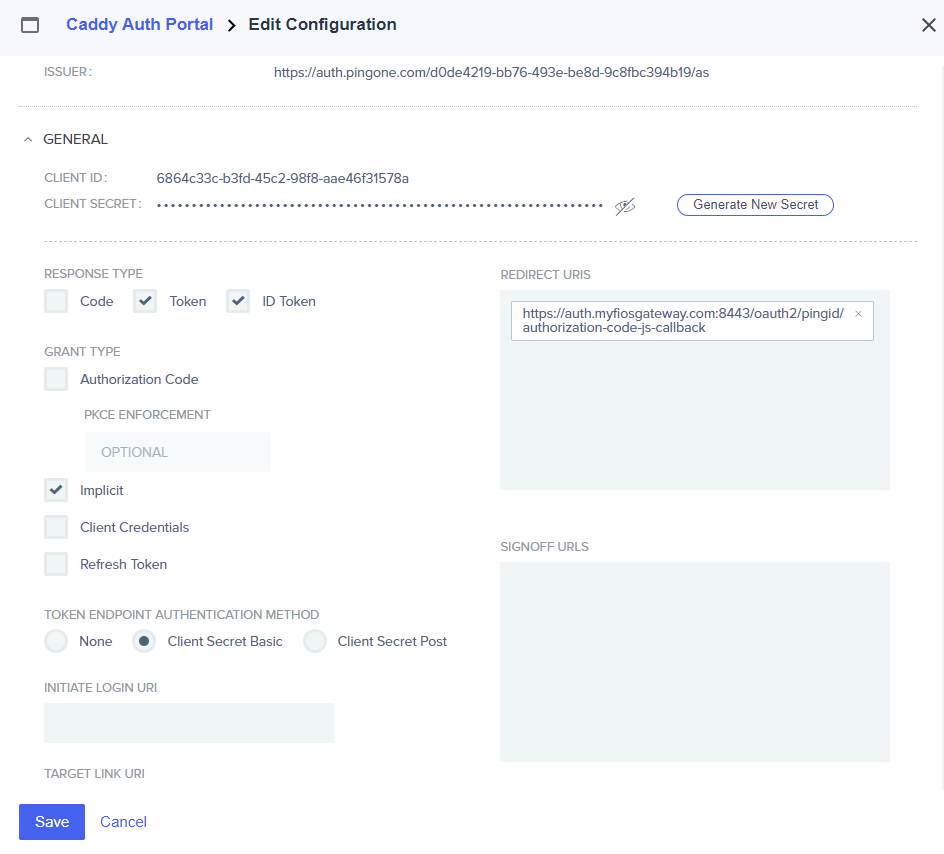
Align the issuer before troubleshooting membership
Ping-branded products and endpoints are not interchangeable. Use the exact discovery and issuer values for the selected service.
| Boundary | Compare | Keep separate |
|---|---|---|
| Browser callback | Public HTTPS origin, portal mount, and AuthCrunch realm | Provider environment or tenant identifier |
| Server discovery and exchange | Reachable discovery/token/key endpoints and client authentication | A browser-only network path |
| Token trust | Exact issuer, client audience, signature, and transaction checks | A configured product/driver name |
| Application grant | Supported claims and deliberate role transform | Successful provider login alone |
Configure AuthCrunch
# caddy-security v1.3.0 / go-authcrunch v1.3.8. Replace auth.example.com.
{
	admin off
	persist_config off
	security {
		oauth identity provider pingid {
			realm pingid
			driver generic
			client_id {env.PINGONE_CLIENT_ID}
			client_secret {env.PINGONE_CLIENT_SECRET}
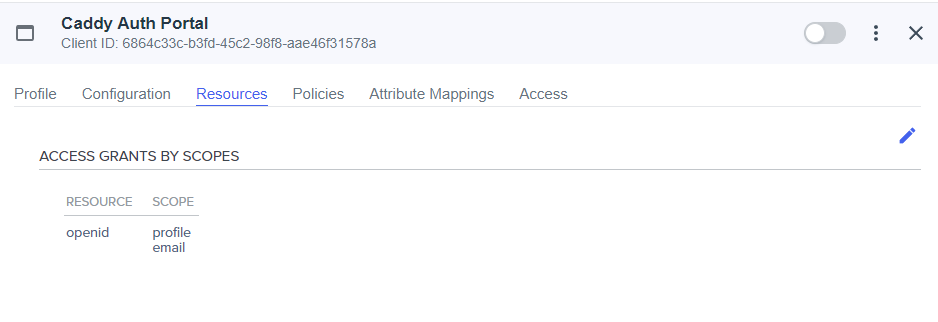
			scopes openid profile email
			response_type code
			issuer {$PINGONE_ISSUER}
			metadata_url {$PINGONE_DISCOVERY_URL}
			login icon text "PingOne"
		}

		authentication portal myportal {
			enable identity provider pingid
			crypto default token lifetime 900
			crypto key sign-verify {env.AUTHCRUNCH_SIGNING_KEY}
			ui {
				links {
					"Example app" /app
					"My identity" /auth/whoami
				}
			}
			transform user {
				match realm pingid
				action overwrite role authp/user
			}
			transform user {
				match realm pingid
				match sub {$PINGONE_ALLOWED_SUB}
				action add role app/member
			}
		}
		authorization policy apppolicy {
			set auth url https://auth.example.com/auth/
			crypto key verify {env.AUTHCRUNCH_SIGNING_KEY}
			validate bearer header
			allow roles app/member
		}
	}
}

auth.example.com {
	route {
		redir /auth /auth/ 308
		authenticate /auth/* with myportal
		@app path /app /app/*
		route @app {
			authorize with apppolicy
			respond "You reached the protected example app." 200
		}
		respond "Open /app to begin." 200
	}
}
PINGONE_ALLOWED_SUB must be the entire exact observed subject. The transform
resets provider roles before granting the selected identity app/member.
PKCE is enabled by the generic driver; keep the application's PKCE policy
compatible. Never enable the old JS callback or implicit token id_token flow
merely to reproduce a screenshot.
If group-based access is preferable, emit a string-array groups claim in the
ID token, inspect its exact values, clear reserved roles, and map only the
intended group to app/member. The generic OIDC guide
explains claim sources and UserInfo limits.
Verify and troubleshoot
Sign in through /auth/oauth2/pingid, inspect /auth/whoami?format=json, and
record the exact subject and realm without logging access tokens. Confirm that
an intended member reaches /app and another valid identity is denied. A
successful provider login alone does not establish application authorization.
Check callback scheme, hostname, port, mount, and realm literally; inspect provider errors and diagnostic logs. Keep client secrets on the server. These examples are parser-verified against the released bundle; console registration, live provider login, consent, and production TLS require verification in your own organization.
Agentic Prompts
Copy a prompt into your LLM to explore this topic. Each prompt prioritizes upstream repository guidance and code over this page, and asks for version-aware reasoning.
Identify the Ping integration
Help me understand Ping Identity.

Primary authorities (take precedence over website documentation):
https://github.com/greenpau/caddy-security/blob/main/AGENTS.md
https://github.com/greenpau/caddy-security/tree/main/.codex/skills
https://github.com/greenpau/go-authcrunch/blob/main/AGENTS.md
https://github.com/greenpau/go-authcrunch/tree/main/.codex/skills
Read each repository's root AGENTS.md first, then any scoped AGENTS.md that
applies to inspected paths. Read the relevant SKILL.md files and follow their
implementation and test references.

Relevant skills to locate: configuration-oauth-providers,
oauth-identity-provider.

Secondary reference:
https://docs.authcrunch.com/docs/authenticate/oauth/backend-oauth2-0010-pingid

If a source is inaccessible, ask me to paste its relevant text. Identify the
versions your answer applies to; main may be newer than my release. Resolve
disagreements using code and tests, and flag unverified claims. Use synthetic
credentials and redacted examples; explain proposed checks before any changes.

Explain PingOne OIDC with the historical pingid realm separately from the
PingID mobile authentication API. Trace provider sign-on/MFA policy, returned
identity, portal transform, and app ACL. Do not infer a dedicated mobile API
from the page’s old route name.
Review environment endpoints
Help me understand Ping Identity.

Primary authorities (take precedence over website documentation):
https://github.com/greenpau/caddy-security/blob/main/AGENTS.md
https://github.com/greenpau/caddy-security/tree/main/.codex/skills
https://github.com/greenpau/go-authcrunch/blob/main/AGENTS.md
https://github.com/greenpau/go-authcrunch/tree/main/.codex/skills
Read each repository's root AGENTS.md first, then any scoped AGENTS.md that
applies to inspected paths. Read the relevant SKILL.md files and follow their
implementation and test references.

Relevant skills to locate: configuration-oauth-providers,
oauth-identity-provider.

Secondary reference:
https://docs.authcrunch.com/docs/authenticate/oauth/backend-oauth2-0010-pingid

If a source is inaccessible, ask me to paste its relevant text. Identify the
versions your answer applies to; main may be newer than my release. Resolve
disagreements using code and tests, and flag unverified claims. Use synthetic
credentials and redacted examples; explain proposed checks before any changes.

Read a confidential PingOne client’s environment/issuer discovery, exact
callback, authorization code, and Client Secret Post setting. Explain browser
versus server reachability and form-body client authentication. Consult
current official PingOne settings rather than assuming a console default.
Choose a membership claim
Help me understand Ping Identity.

Primary authorities (take precedence over website documentation):
https://github.com/greenpau/caddy-security/blob/main/AGENTS.md
https://github.com/greenpau/caddy-security/tree/main/.codex/skills
https://github.com/greenpau/go-authcrunch/blob/main/AGENTS.md
https://github.com/greenpau/go-authcrunch/tree/main/.codex/skills
Read each repository's root AGENTS.md first, then any scoped AGENTS.md that
applies to inspected paths. Read the relevant SKILL.md files and follow their
implementation and test references.

Relevant skills to locate: configuration-oauth-providers,
oauth-identity-provider.

Secondary reference:
https://docs.authcrunch.com/docs/authenticate/oauth/backend-oauth2-0010-pingid

If a source is inaccessible, ask me to paste its relevant text. Identify the
versions your answer applies to; main may be newer than my release. Resolve
disagreements using code and tests, and flag unverified claims. Use synthetic
credentials and redacted examples; explain proposed checks before any changes.

Compare a realm-scoped exact subject allowlist with an
administrator-controlled ID-token groups array. Explain supported generic
claim paths and optional UserInfo limitations. Keep application membership
distinct from provider MFA completion.
Diagnose a PingOne failure
Help me understand Ping Identity.

Primary authorities (take precedence over website documentation):
https://github.com/greenpau/caddy-security/blob/main/AGENTS.md
https://github.com/greenpau/caddy-security/tree/main/.codex/skills
https://github.com/greenpau/go-authcrunch/blob/main/AGENTS.md
https://github.com/greenpau/go-authcrunch/tree/main/.codex/skills
Read each repository's root AGENTS.md first, then any scoped AGENTS.md that
applies to inspected paths. Read the relevant SKILL.md files and follow their
implementation and test references.

Relevant skills to locate: configuration-oauth-providers,
oauth-identity-provider.

Secondary reference:
https://docs.authcrunch.com/docs/authenticate/oauth/backend-oauth2-0010-pingid

If a source is inaccessible, ask me to paste its relevant text. Identify the
versions your answer applies to; main may be newer than my release. Resolve
disagreements using code and tests, and flag unverified claims. Use synthetic
credentials and redacted examples; explain proposed checks before any changes.

Help me separate wrong environment discovery, Basic-versus-Post client
authentication, callback mismatch, missing ID-token email/group, and
post-login 403. Ask for redacted metadata and claim shapes. Preserve state,
PKCE, nonce, and signature trust.
Verify the intended access boundary
Help me understand Ping Identity.

Primary authorities (take precedence over website documentation):
https://github.com/greenpau/caddy-security/blob/main/AGENTS.md
https://github.com/greenpau/caddy-security/tree/main/.codex/skills
https://github.com/greenpau/go-authcrunch/blob/main/AGENTS.md
https://github.com/greenpau/go-authcrunch/tree/main/.codex/skills
Read each repository's root AGENTS.md first, then any scoped AGENTS.md that
applies to inspected paths. Read the relevant SKILL.md files and follow their
implementation and test references.

Relevant skills to locate: configuration-oauth-providers,
oauth-identity-provider.

Secondary reference:
https://docs.authcrunch.com/docs/authenticate/oauth/backend-oauth2-0010-pingid

If a source is inaccessible, ask me to paste its relevant text. Identify the
versions your answer applies to; main may be newer than my release. Resolve
disagreements using code and tests, and flag unverified claims. Use synthetic
credentials and redacted examples; explain proposed checks before any changes.

Create cases for selected subject/member, another valid identity, wrong group,
reserved-role injection, and fresh login after mapping changes. Include portal
logout versus PingOne SSO. Explain what live registration checks add beyond
local OIDC fixtures.
Source Code References
Start with the code search, then follow the parser, runtime, and tests relevant
to this topic. These links target main; use GitHub's branch/tag selector to
compare them with your installed release.
- Search this topic in both repositories — searches topic-specific symbols and paths across both codebases.
- caddy-security: caddyfile_identity_provider_oauth.go — adapts OAuth/OIDC provider settings, scopes, endpoints, and trust options.
- go-authcrunch: pkg/idp/oauth/config.go — validates generic and named-driver defaults and endpoint settings.
- go-authcrunch: pkg/idp/oauth/provider.go — loads discovery metadata, provider readiness, and driver setup.
- go-authcrunch: pkg/idp/oauth/authenticate.go — handles authorization callbacks, token exchange, and identity completion.
- go-authcrunch: pkg/idp/oauth/claim_parser.go — maps supported token claims into the normalized provider identity.
- go-authcrunch: pkg/idp/oauth/claim_parser_test.go — tests supported claim paths and rejected value shapes.