Authentication + authorization for Caddy
Who gets in?
You write the rules.
Connect identity, login, and access policies with AuthCrunch. Follow a request below, then build the same flow in Caddy.
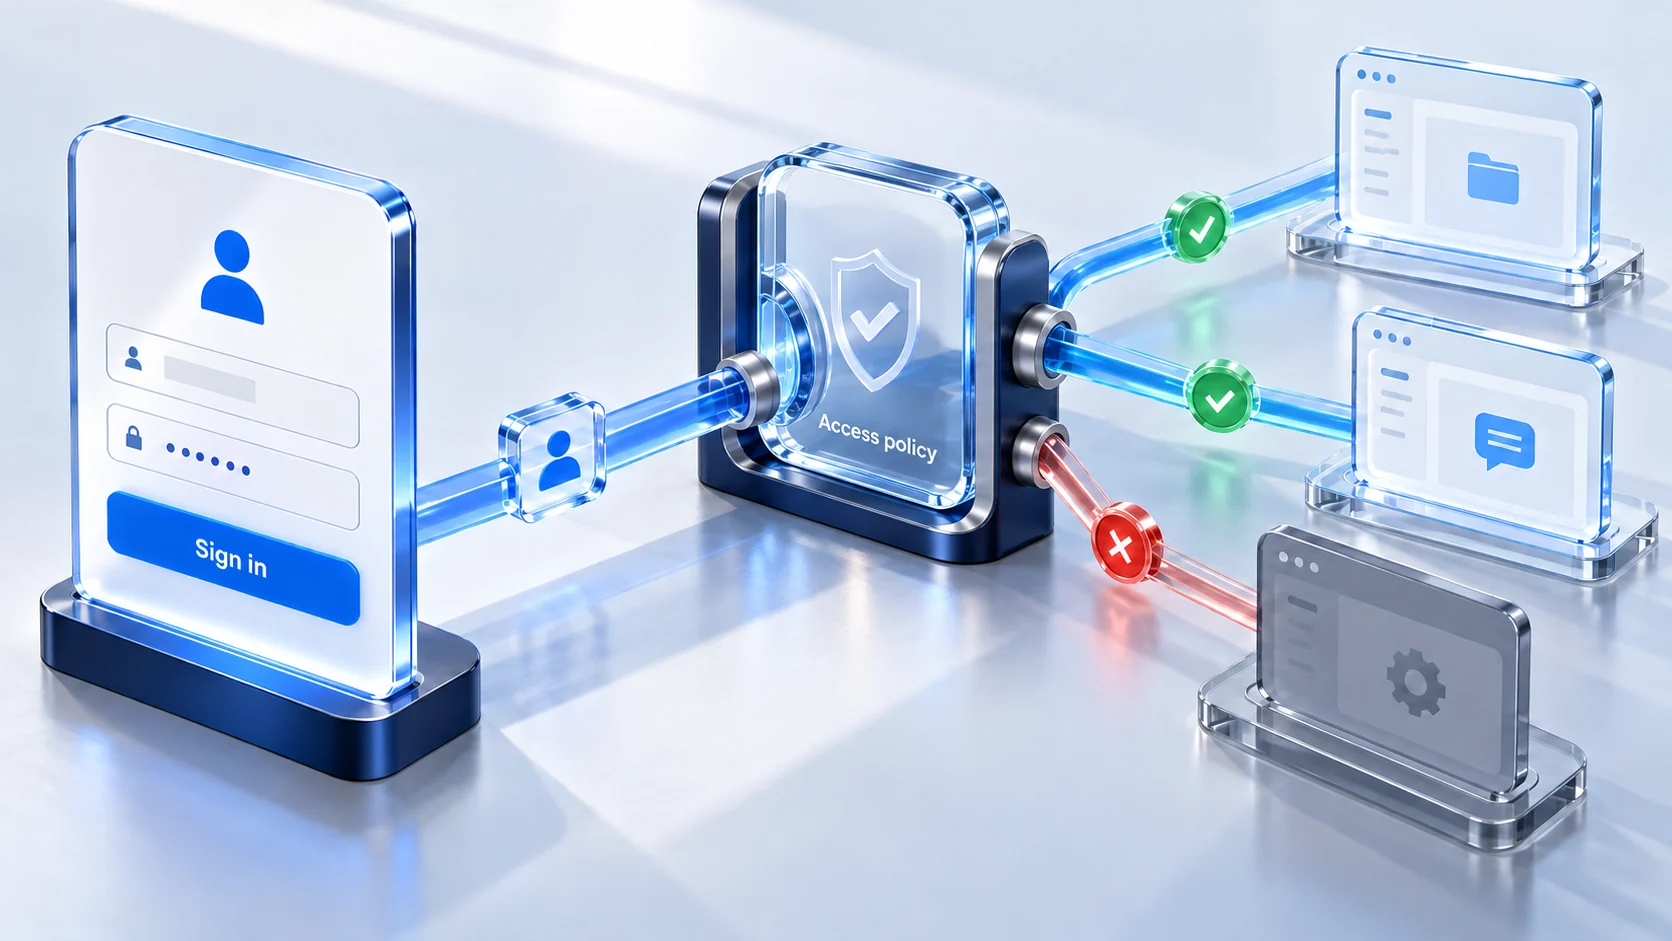
01 / The visitor
authp/userapp/member02 / Caddy + AuthCrunch
allow roles authp/admin authp/user03 / The decision
The app is yours to use.
Alice has authp/user. The policy allows the request to reach the app.
Your first working setup
Four steps. A working front door.
- Get the right buildInstall the ready-to-run Caddy distribution and verify its modules.Open the guide
- Make your first loginRun the local portal. Follow real screenshots through the login flow.Open the guide
- Connect identity to accessSee how the portal, cookies, and application policy fit together.Open the guide
- Prove your policy worksCheck allowed access, denied access, and the next request after logout.Open the guide
Explore the moving parts
What are you working on?
Choose a part of the flow. Find the guides that move you forward.
01 / Identity
Start with the people signing in.
Connect local users or an external identity provider. Understand which claims arrive before you grant access.
Explore identity guidesChoose the right starting point
Different apps.
Different ways to sign in.
A portal with profile pages and a policy that signs users in directly have different responsibilities. Compare the flows before choosing yours.
Understand the login modelsAuthentication establishes identity.
Your policy decides what that identity may access.
Two ways to protect an app
- Sign in through the portalLocal users or an identity provider
- Receive an access tokenThe portal records the user's claims
- Check access to the appYour policy evaluates those claims
Use a portal for login, local MFA and profile pages. Attach an authorization policy to the protected app.
Keep learning by doing
Start local. Follow the whole request.
One Caddyfile, two demo users, and an application you can protect.